HTTPS protects the connection between a browser and the server it communicates with. It helps prevent outsiders on the network from reading or secretly changing the information travelling over that connection. It does not prove that a business is honest or that every part of its website is secure.
For a business owner, that distinction matters. Enabling HTTPS is necessary, but it is one part of website security rather than a certificate that the whole business is safe.
What happens to the connection
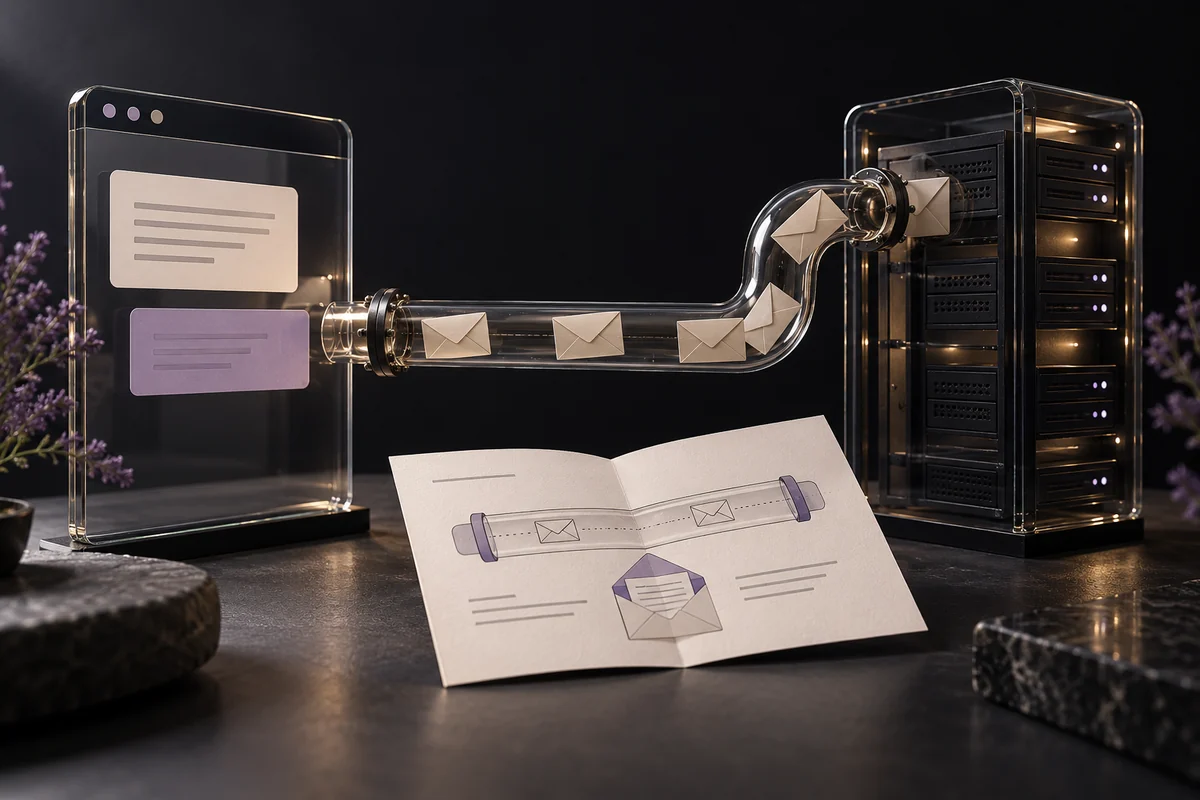
HTTPS is HTTP carried over Transport Layer Security, usually shortened to TLS. The browser and server establish a protected connection before exchanging the website's requests and responses.
TLS provides encryption, integrity checks and server authentication. In ordinary terms, it protects the message in transit, helps detect changes made along the way and lets the browser check the server's certificate for the domain being visited. MDN's TLS overview explains those three functions.
The protection applies to the connection's contents. For example, a submitted form or account request is protected while travelling across that connection. It is not the same thing as encrypting every copy of the data wherever it may later be stored.
A certificate does not verify the sales pitch
A valid certificate helps the browser establish a connection to the domain in its address bar. It does not verify product quality, refund promises, customer reviews or the identity of every person operating the business.
A deceptive site can use HTTPS too. That is why visitors still need to check the actual domain, evaluate the business and be cautious about unexpected payment or login requests.
Likewise, a business should not display a generic secure-site badge as if it were an independent audit of all its systems. Describe specific protections accurately. Our guide to building trust online explains the separate role of honest evidence and clear information.
Where the protection ends
Once the intended endpoint receives information, HTTPS does not decide what happens next. Access controls, application logic, storage practices and staff permissions determine how it is handled.
If a website uses a proxy or content delivery network that terminates TLS, there can be another connection between that service and the origin server. The configuration of that connection also needs review. The browser's protected connection alone does not describe the complete infrastructure.
A compromised administrator account or malicious script delivered by the site can also cause harm despite HTTPS. Encryption can faithfully carry content from a compromised endpoint. It cannot establish that the content is harmless.
HTTPS does not make browsing completely anonymous
Protecting request contents does not make all surrounding network information invisible. The network can still observe connection metadata, and destination information may remain visible depending on the protocols and services used.
The website receiving your request also needs to process information to deliver the page. Its analytics, cookies, server logs and third-party services introduce separate privacy questions.
For business owners, the practical lesson is to explain actual data practices rather than treating HTTPS as a complete privacy policy. For visitors, it is a reason to assess what information you submit and who receives it.
Avoid mixed content and certificate problems
A page served through HTTPS should also load its images, scripts and other resources securely. Mixing an HTTPS page with HTTP resources can undermine protection and lead to browser blocking or upgrades.
Ask whoever manages the website to check certificate renewal, secure resource URLs, the HTTP-to-HTTPS redirect and the connection to the origin where relevant. Review changes before enabling stricter settings across subdomains.
Do not train customers to ignore certificate warnings. Investigate the cause and fix the configuration. A working homepage is not enough if checkout, administration or another important hostname has a different problem.
What to ask your website provider
- Who manages certificates and renewal failures?
- Are the browser connection and any proxy-to-origin connection protected appropriately?
- Have forms, checkout, assets and redirects been tested?
- Who responds if a warning or security incident occurs?
- What protects accounts, software and stored information beyond TLS?
MDN's HTTPS definition is a useful short reference for the connection itself. For the wider responsibilities, read our small business website security guide .
HTTPS should be a normal part of a professionally managed website. Understand its boundary, keep it functioning and combine it with the operational protections that the rest of the website requires.